
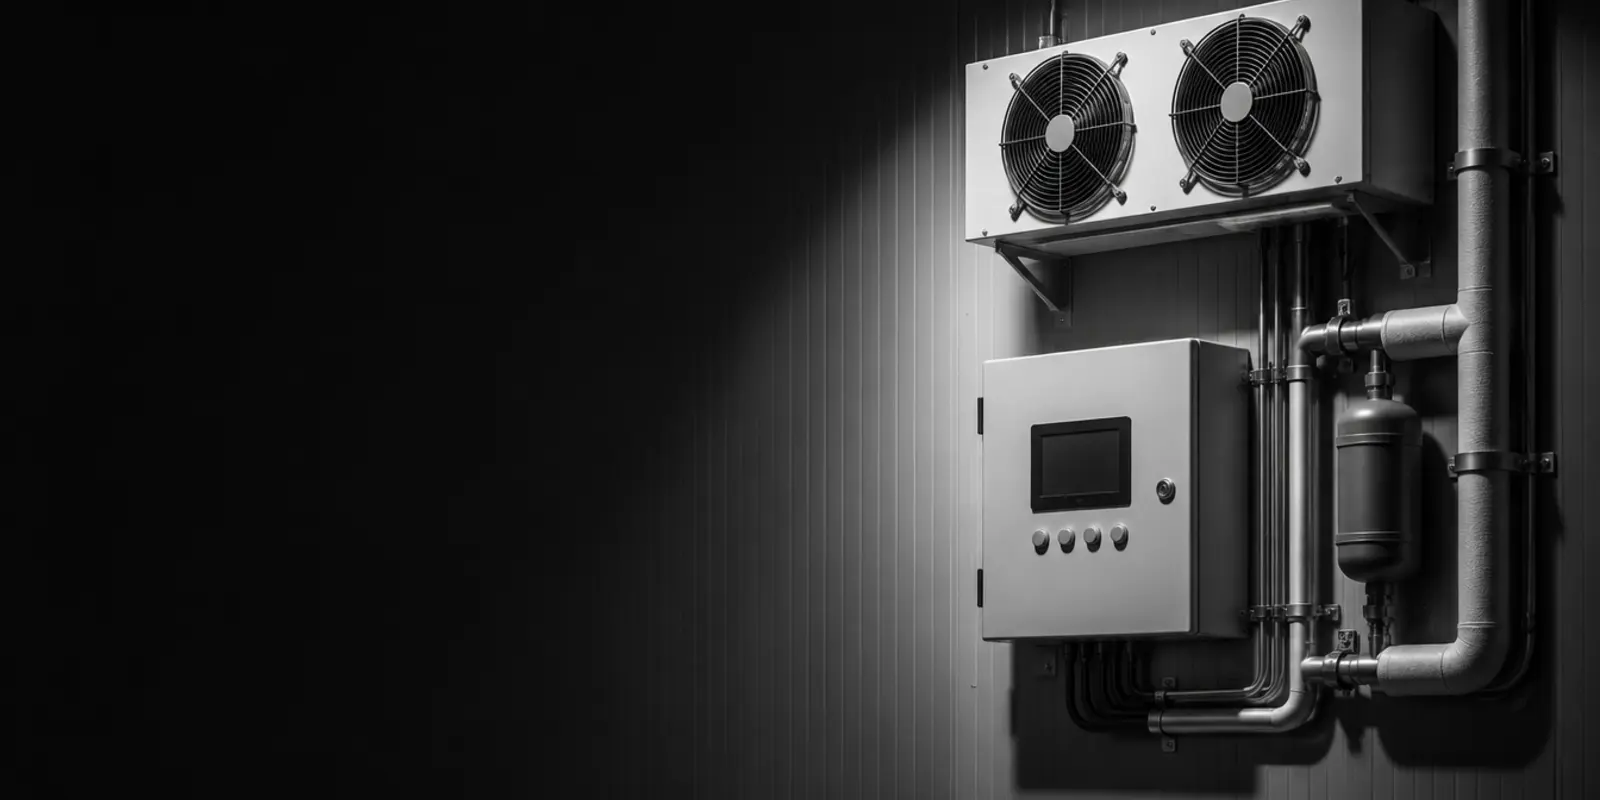
This week the FBI warned American supermarkets to take their cooling systems off the internet. The reason: cooling installations that turn out to be directly reachable through the internet, often without any protection at all. It may sound like a story from far away, but the situation in Dutch wholesale, food production and transport is just as real. Cooling is exactly the kind of system that used to be managed locally and is now read out remotely, often by the supplier of the installation itself.
A warning that reaches beyond supermarkets
Cooling systems have become smarter over the past years. Temperature, faults and energy use are monitored remotely, often by the installer or a specialised party. Useful, because it means faults get noticed faster. But to allow that remote monitoring, a system needs to be connected to the internet. And that connection is not always properly shielded.
For a wholesaler with cold storage, a food producer with freezer rooms or a transport company with refrigerated trailers, the same principle applies. The moment a cooling system is connected to the internet, it can in theory be reached from the outside. Not necessarily because someone specifically targets your business, but because these kinds of systems are scanned worldwide for weak spots.
The real risk is not the hack, it’s the outage
This is not about a dramatic hacking story. It is about continuity. If a cooling system is taken over, switched off or misconfigured, stock spoils. That means lost revenue, possible damage to your reputation with customers who have strict chain requirements, and in some sectors trouble with certification or food safety.
The point is that this risk already exists without anything malicious happening. A misconfigured internet connection, a forgotten factory-default password, a supplier who kept access after the contract ended: these are all ways a cooling system becomes vulnerable unintentionally. The FBI warning is a nudge to look into this now, rather than after an incident.
Measure first: find out what is actually exposed
Before you can decide what to do, you need to know what you have. That sounds obvious, but in practice few businesses know exactly which operational systems are connected to the internet. Cooling installations, freezer rooms, loading dock controls, climate control in a production hall: these are all systems that often fall outside the view of the regular ICT department, because they were connected by the installer.
Concretely, this means: ask your cooling installation supplier whether there is remote monitoring, and how that connection is secured. Ask who has access, and whether that access is still up to date. And have your network mapped by your ICT partner, so it becomes visible which devices communicate externally. You cannot make policy about something you cannot see.
From exposure to a documented scenario
A properly shielded connection is a good first step, but no guarantee that cooling will never fail. A power outage, a broken compressor or human error can always happen, regardless of internet risk. That is why this subject also belongs in your business continuity plan.
Write down what happens if a cooling system fails. Who is alerted first, who is allowed to physically access the installation, within what time a backup system or temporary solution must be active, and who decides whether stock needs to be written off. This is not a theoretical exercise. It is the difference between a night full of panic and a procedure everyone already knows.
What you can do this week
Start with an overview of all cooling and climate systems that are managed or monitored remotely. Ask for each system who has access and how that access is secured. Discuss with your ICT partner whether a network scan is needed to find hidden connections. And make sure cooling failure is a documented scenario, with an owner and concrete steps, instead of something you simply hope never happens.
A few questions we’re often asked
Do we need to take our cooling installation off the internet completely?
Not necessarily. Many installations benefit from remote monitoring, for example for early fault detection. The point is that the connection is deliberately set up and shielded, rather than left open without anyone knowing.
Our cooling installation is managed by the supplier, so is this really our problem?
Legally and operationally, yes. You carry the consequences if stock spoils, regardless of who manages the connection. It is therefore wise to make explicit agreements with the supplier about access and security, and to document them.
How do I know if this applies to our business if I have no technical knowledge of networks?
You do not need to judge this yourself. A short inventory by your ICT partner will show which systems connect to the internet and who has access to them. That gives you a concrete picture within a few days, instead of a guess.
Does this belong to ICT security or to business continuity?
Both, but in this order: first map out what is technically exposed, then document what happens if cooling fails anyway. Security reduces the chance of failure, a continuity plan makes sure you are prepared if it happens regardless.
Want to know which operational systems in your business are connected to the internet, and whether a cooling outage is documented as a scenario? We are happy to think along, from the domain of business continuity rather than loose technical fixes.
